

Overview
The Blacklisted Assets section allows you to exclude specific assets from monitoring, scans, and risk signal evaluations. This helps security teams eliminate false positives, ignore non-relevant infrastructure, and maintain a clean and actionable attack surface view.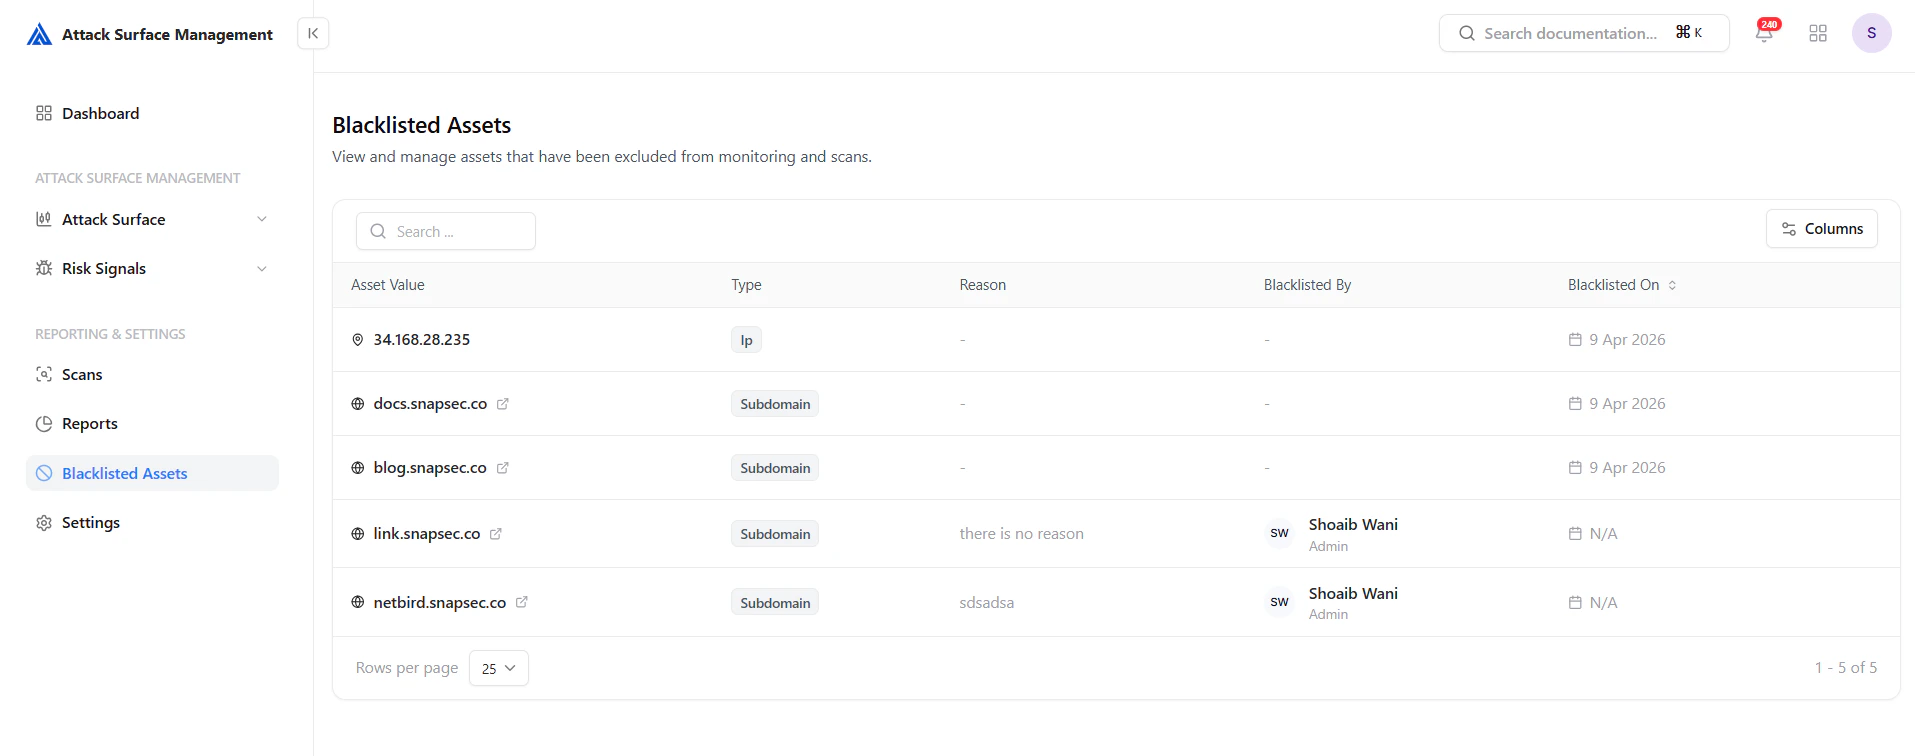
Blacklisted assets table showing excluded IPs and subdomains
Why Blacklist Assets?
Not all discovered assets require monitoring. Blacklisting is useful when:- 🧪 Assets are used for testing or staging
- 🔁 Assets are owned but intentionally exposed
- 🚫 Assets are out of scope for security monitoring
- ⚠️ Assets generate repeated false positives
Blacklisted Assets Table
The table provides a centralized view of all excluded assets.Fields Explained
How Blacklisting Works
Once an asset is blacklisted:- It is excluded from scans
- It does not appear in Risk Signals
- It is ignored in exposure detection
- It is removed from security prioritization workflows
Workflow Example
- Identify an asset generating noise or not relevant
- Add it to the Blacklist
- Future scans ignore the asset
- Risk Signals no longer include it
- Security team focuses on real threats
Best Practices
- 🎯 Only blacklist assets that are confirmed non-critical
- 📝 Always provide a reason for traceability
- 🔍 Periodically review blacklisted assets
- 🔁 Re-include assets if their risk profile changes
Value to Security Teams
From Noise to Clarity
Discover → Filter → Focus → Secure Blacklisting ensures your attack surface reflects what truly matters.Explore Live Demo
Explore ASM Live — No Signup Needed
Instantly explore how Snapsec Attack Surface Management (ASM) detects exposures, filters noise, and enables real-time security decisions — all in one unified platform.